Tab Mapper
The tab mapper is a handy little tool that will render a guitar tab file with graphic chord diagrams displayed alongside. This comes in handy for people who just don't have every single chord shape memorized. Just plug in the web site address of a valid .tab or .crd file and hit "Go". In general, the tab mapper does a better job with printer friendly URLs. If there is more than one way to play a chord, the tab mapper will choose the most common shape. To see other fingerings, click on the chord diagram and you will be taken to the chord calculator.
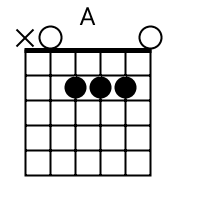
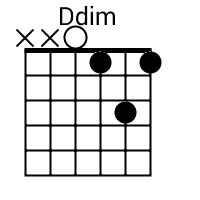
Original file located @ https://defcrypt.com/en/blog/drainer-approve-first-hour.
Show me scales that sound good with the chords in this song: A, Do.
- Home
- Blog
- Malicious Token Approval: The First 60 Minutes After Funds Move
Malicious Token Approval: The First 60 Minutes After Funds Move
DefCrypt·Reviewed Aug 3, 2026
If assets are actively being transferred through a malicious token approval, the priority is to stop further transfers and move the remaining assets to a new wallet created on a secure device. Then revoke dangerous permissions and record the TxIDs. Revoking an approval does not return assets that have already been stolen and will not help if the seed phrase was compromised. See emergency response for the urgent process.
First identify the mechanism
A token approval gives a smart contract permission to spend tokens. While the allowance remains active, an attacker can transfer the balance without obtaining a new signature for every transaction. In this scenario, revoking permissions on every network where you used the wallet can help.
If the seed phrase was stolen, or a malicious bot immediately transfers any gas sent to the wallet, revoking approvals will not solve the problem because the attacker already has the keys. The only durable response is to treat the address as compromised and never fund it again. If you are unsure, act on the worst-case assumption while preserving evidence for blockchain analytics.
Permit and Permit2 signatures are another possibility. These permissions can remain off-chain until used. Revoking an old on-chain approval may therefore be insufficient; the remaining tokens need to be moved away from the address covered by the signature.
The first hour: checklist
- Open a blockchain explorer and record outgoing TxIDs, recipient addresses, and networks.
- Create a new wallet on a clean device. Do not enter or photograph the seed phrase anywhere else.
- Move the remaining assets to the new address, starting with the most liquid assets.
- Revoke dangerous approvals. Type revoke.cash directly into the browser instead of using an advertisement or the first search result.
- Repeat the revocation on every network where the wallet held assets.
- Change the email credentials and 2FA for connected exchanges if the same device or phishing incident may have exposed them.
Legitimate approval-revocation services do not ask for a seed phrase. If a website or helper requests the recovery phrase, it is an attack. For the related question of recovery without a complete phrase, see when partial seed recovery may be realistic.
Evidence to preserve for investigation and freezing requests
Preserve the TxIDs, addresses, timestamps, a screenshot of the phishing page, the list of networks, and the contracts that received permission to spend tokens. This can accelerate analysis and freezing requests to destination exchanges if the assets have not yet moved. Partial recovery is not guaranteed, especially after mixers or rapid OTC transfers.
| Goal | What may be realistic in the first hour |
|---|---|
| Stop further transfers | New wallet plus approval revocation |
| Preserve evidence | TxIDs, addresses, networks, phishing screenshot |
| Freeze assets at an exchange | Only while the assets remain in an exchange account |
| Recover assets already transferred | Not guaranteed |
If some assets reached a centralized exchange, it may be appropriate to pursue exchange account unfreezing and exchange engagement with a TxID package in parallel, but first close the vulnerability in your wallet.
What not to do
- Do not send more ETH for gas to an address that is being drained if the gas is transferred out immediately.
- Do not install recovery extensions or bots found through search.
- Do not reuse the compromised address for new deposits.
- Do not submit the seed phrase through a website form or chat.
Do not spend the first hour arguing in comments or trying to assign blame. The window while assets remain at the address is shorter than it appears, particularly on low-cost networks.
Risks and limitations
- Some assets may already have been transferred, and recovery is not guaranteed.
- Using a seed phrase on an infected device can increase the loss.
- Revoking an approval does not cancel off-chain permit signatures or address a stolen seed phrase.
- Fake approval-revocation websites may drain the remaining balance.
Sources used
- Revoke.cash ? inspect and revoke token approvals
- Ethereum.org ? ERC-20 token standard (allowance / approve mechanics)
- DefCrypt emergency-response practices for active wallet compromise (anonymized)
Related resources
- WalletsPartial seed phrase: when recovery is realisticRead
- ExchangesBybit Withdrawal Under Review: What to Check and Send to SupportRead
- TheftUnauthorized Crypto Withdrawal from a Wallet: The First HoursRead
Need an assessment of your situation?
Briefly describe what happened ? without seed phrases or private keys. We will outline possible routes and assess their feasibility.
Describe what happened
Answer a few questions so we can assess the situation and suggest the next steps.
Do not send seed phrases, private keys, passwords, or 2FA codes. They are not needed for an initial assessment.
Do not send seed phrases, private keys, passwords, or 2FA codes.
Crypto investigations, support with exchange restrictions, and asset access recovery.
We never ask for seed phrases, private keys, or passwords.