Tab Mapper
The tab mapper is a handy little tool that will render a guitar tab file with graphic chord diagrams displayed alongside. This comes in handy for people who just don't have every single chord shape memorized. Just plug in the web site address of a valid .tab or .crd file and hit "Go". In general, the tab mapper does a better job with printer friendly URLs. If there is more than one way to play a chord, the tab mapper will choose the most common shape. To see other fingerings, click on the chord diagram and you will be taken to the chord calculator.
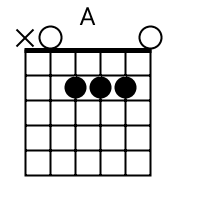
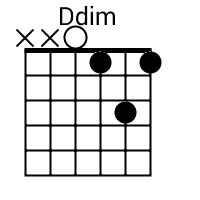
Original file located @ https://defcrypt.com/en/blog/company-lost-crypto-what-businesses-should-do.
Show me scales that sound good with the chords in this song: A, Do.
- Home
- Blog
- Company Lost Crypto: What Businesses Should Do
Company Lost Crypto: What Businesses Should Do
DefCrypt·Reviewed Aug 26, 2026
If a company lost crypto, the first 24 hours are about stopping further outflow, preserving TxIDs, and keeping communications tight. A treasury incident is not the same as theft from a personal wallet: signers, authority to act, and freeze requests from a legal entity follow a different path. See emergency response for the urgent route.
How a corporate incident differs from private theft
A private case is usually one wallet, one signer, and a short loop: close the gap, then preserve evidence. A company also has treasury wallets, multisig, rebalancing bots, exchange API keys, and several employees with access. The loss may be external (phishing, a malicious token approval, a leaked seed phrase) or internal: one signer is compromised. The personal-wallet checklist is in hacked crypto wallet: what to do; this article covers the layer that a private case does not have.
The second axis is communications. A public project cannot stay silent forever: the chain is visible to outside observers. An early "we were hacked" post without facts or a freeze request often backfires: counterparties panic, and attackers speed up withdrawals. Name a small circle in advance: who speaks to exchanges, who speaks to counsel, who speaks to investors ? and what is not published until the TxID package exists.
The third axis is the form of the request. Platforms treat an approach from a legal entity differently: they expect proof of authority, company identifiers, and a coherent route report, not a chat screenshot. That is not a promise that assets will be frozen; it is a different entry into the same process described in freezing stolen crypto on an exchange.
The first 24 hours: checklist
- Stop further outflow: revoke dangerous token approvals, move the remainder to a new key set, and disable bots and scripts that used the old keys or API credentials.
- Record TxIDs, networks, addresses, block times, affected treasury addresses, and access logs for signing if you have them.
- Define a tight communications circle: one channel to exchanges, one to counsel, and a ban on unofficial social posts.
- Check whether a compromised multisig signer is still active; change the threshold and key set if needed.
- Assemble authority to act for the company before a mass email to every partner.
- Do not enter a seed phrase or send API secrets in a ticket, a chat, or a helper found through search.
In parallel, assess whether the assets reached a centralized-exchange deposit: the window for a hold request is shorter than an internal meeting cycle. Mapping hops belongs in blockchain analytics, not in a single explorer screenshot. If the wallet gap is still open, close it first ? every hour can add new outgoing transfers.
Freeze requests, partners, and the legal track
A freeze request asks a platform to hold a deposit while the assets remain in its accounts. It does not reverse a blockchain transfer. From a company, platforms typically want a coherent package: TxIDs, the route, the mechanism (phishing, approval, insider), and proof of authority. The exchange decides; you do not set its response time. Anonymized write-ups without promised outcomes are in case studies.
| Objective | What may be realistic in the first day |
|---|---|
| Stop further outflow | New key set, stop bots and approvals |
| Evidence package | TxIDs, addresses, times, access logs |
| Freeze request | Only while assets remain in a platform account |
| Full recovery | Not guaranteed |
Partners and investors are better served by a short factual note after the first evidence capture than by silence until a leak or a panicked post. The legal layer ? authority, contracts, a report to authorities ? is a separate track, not a substitute for stopping the loss; see a lawyer after crypto theft. A public statement before the evidence package rarely speeds up a freeze.
What not to do
- Do not publish raw incident details until the TxID package exists and destination platforms have been contacted.
- Do not leave a compromised key in the multisig "for later."
- Do not pay a recovery guarantor or put a seed phrase in a ticket.
- Do not confuse freezing someone else's deposit with unfreezing your own exchange account.
Do not spend the first day assigning blame in chats. The window while remainder sits on an address or an exchange deposit is shorter than internal alignment. Stop the outflow and preserve evidence first; then shape the public narrative.
Risks and limitations
- Some assets may already have been withdrawn, and recovery is not guaranteed.
- A premature public post can speed up withdrawals and complicate freeze requests.
- Sharing a seed phrase, keys, or API secrets in a ticket or with a helper increases the loss.
- If a compromised signer remains in the multisig, outflow can continue.
- A freeze at an exchange is the platform's decision; the window before withdrawal can close in hours.
Sources used
- FBI IC3 ? Cryptocurrency: what to report after theft or scam
- FBI IC3 PSA ? false cryptocurrency recovery services (up-front fee schemes)
- Chainalysis ? What Is Asset Seizure and Forfeiture? (holds at custodians)
- DefCrypt emergency-response practices for corporate crypto incidents (anonymized)
Related resources
- TheftCrypto Wallet Hacked: Where to StartRead
- TheftFreezing Stolen Crypto on an Exchange: Requests and EvidenceRead
- LegalWhen to Involve a Lawyer After Crypto TheftRead
Need an assessment of your situation?
Briefly describe what happened ? without seed phrases or private keys. We will outline possible routes and assess their feasibility.
Describe what happened
Answer a few questions so we can assess the situation and suggest the next steps.
Do not send seed phrases, private keys, passwords, or 2FA codes. They are not needed for an initial assessment.
Do not send seed phrases, private keys, passwords, or 2FA codes.
Crypto investigations, support with exchange restrictions, and asset access recovery.
We never ask for seed phrases, private keys, or passwords.